
Diffing for Intent: Stopping Supply-Chain Malware at the Code-Signing Gate
SolarWinds, 3CX, and XZ Utils were different intrusions but shared one method: the attacker changed a small part of an otherwise legitimate binary. Because the tampered file had never been seen before, it carried no known-bad signature, and it often arrived already inside a trusted build. Signature-based antivirus asks “does this match known malware?”, the wrong question when the threat is a new modification to software the organisation builds itself.
We take a different starting point: rather than matching known threats, we ask whether a binary changed in a way that suggests tampering or new capability, and we run that check just before code signing. A signature is a trust stamp downstream systems honour without re-checking, so pre-signing is the last chance to stop tampering before it ships. The pipeline has two steps: first we diff the compiled binary against a known-good baseline, using structural and mnemonic-level comparison to isolate what changed while tolerating recompilation and relocation noise. Then a large language model reads the disassembly of only the changed code (or the behaviourally relevant code for net-new binaries) and judges intent: process injection, C2 beaconing, credential access, persistence, or a flipped authorization check etc.
One model verdict isn’t enough for a gate whose expensive error is a false negative. A multi-agent design improves reliability: separate agents for change-consistency and absolute-intent analysis, a red-team/blue-team step where one agent must prove the change is malicious before a clean verdict is allowed, and a final analyst agent that decides. We hold to one rule: a non-deterministic model should not own the sign-or-block decision. Deterministic integrity evidence (checksum, entry-point, and hardening regressions) and any confirmed-malicious finding form a hard floor the model can escalate but never overrule.
We evaluated the approach on thousands of real Windows, Linux, and macOS binaries. It caught the real XZ Utils backdoor (CVE-2024-3094) and several simulated supply-chain implants, including a trojanized open-source library and binaries carrying outbound C2 and covert DNS exfiltration, while clearing benign open-source upgrades.
The session focuses on detection lessons and open problems: evasion that structural diffing can miss (for instance, operand-level micro-patches), the difficulty of judging a binary with no baseline, coverage across PE, ELF, and Mach-O, and the lack of any public benchmark for LLM-based binary supply-chain detection. Attendees leave with a concrete pre-signing architecture, a clear view of where LLM reasoning helps and where deterministic controls must stay in charge, and open evaluation gaps.
Key Takeaways
- Why signature-based AV structurally misses novel supply-chain modifications, and why the moment before signing is a good place to catch them.
- A practical architecture that pairs baseline diffing (to find what changed) with LLM reasoning over disassembly (to judge why it changed).
- How multi-agent orchestration, combining adversarial review with deterministic floors, is built for a gate where a false negative is the expensive mistake, and why the model does not get the final say.
- The real evasion and evaluation problems: operand-level micro-patches, no-baseline binaries, cross-platform analysis, and the missing public benchmark for this problem.
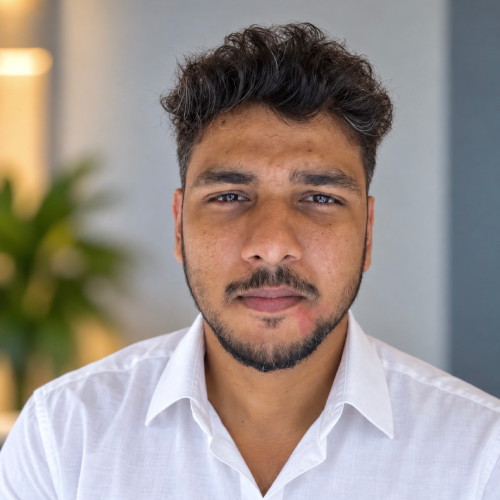
Rishal – Adobe
Rishal Dwivedi is a security researcher and engineer with 10+ years of experience in cybersecurity, specializing in vulnerability research. He began his security journey through bug bounty hunting, discovering and reporting vulnerabilities in products and platforms from organizations including Microsoft, Yahoo, Google, Facebook, Twitter, PayPal, Apple, and others.
Previously, Rishal worked as a Security Researcher at Microsoft and as a Senior Application Security Engineer at Qualys. He also led security research at Loginsoft, focusing on fuzzing, binary analysis, and zero-day discovery.
At Adobe, Rishal focuses on vulnerability discovery at scale, fuzzing, and application security. He has developed an in-house vulnerability discovery harness that leverages LLM-based code reasoning to identify and analyze potentially vulnerable code, validate findings, and assist with proof-of-concept generation.
His research interests include vulnerability discovery, fuzzing, malware analysis, application security, and security automation. Rishal has presented security research at DEF CON 30 Demo Labs and continues to explore practical techniques and tooling for discovering and analyzing vulnerabilities in complex software systems.
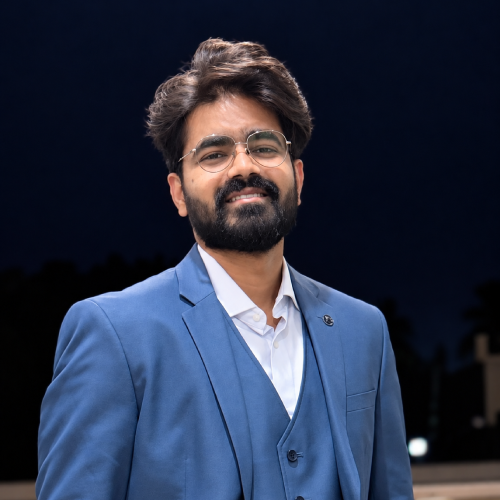
Kushal – Abode
Kushal Rajput is a Senior Software Engineer at Adobe with 8+ years of experience in distributed systems, security platforms, and large-scale software engineering. He is passionate about diving deep into complex systems, identifying challenging problems, and building innovative solutions.
Before joining Adobe, Kushal worked at Amazon on distributed systems supporting global marketing platforms responsible for delivering more than 50 billion notifications annually. His work focused on designing and evolving large-scale data-processing and backend systems.
At Adobe, Kushal works within the Cybersecurity organization, where he helps maintain and evolve a centralized code-signing platform that processes around 2,000 binaries every day across Windows, Linux, and macOS. His work focuses on strengthening software supply-chain security, including the development of a binary-diffing and multi-agent LLM-based detection system that analyzes changes in compiled binaries to identify potentially malicious intent before software reaches the signing gate.
Kushal’s interests include distributed systems, cybersecurity, AI engineering, and building practical solutions to difficult problems at scale.