
Dead Container Walking: Post-Incident Analysis When Your Workload Is Already Gone
In Kubernetes, compromised containers often disappear before investigators can respond, leaving no disk, process state or live system to inspect.
This talk explores how attackers exploit ephemeral workloads and why traditional forensic approaches fail in cloud-native environments.
Attendees will leave with a blueprint for building forensically ready clusters where even the most ephemeral workloads leave a permanent mark.
Benefit to Eco-system
Forensic Readiness Standardization: Transforms the industry from reactive cleanup to proactive readiness by defining a clear standard for capturing volatile evidence in staging Kubernetes environments.
Bridging Security and Observability: Unite DevSecOps teams by demonstrating how SREs and platform engineers can leverage existing observability signals to conduct active security investigations.
Democratizing threat detection: Lowers the barrier to entry for robust security by showing how open source tools provide enterprise level forensics capabilities without expensive proprietary software.
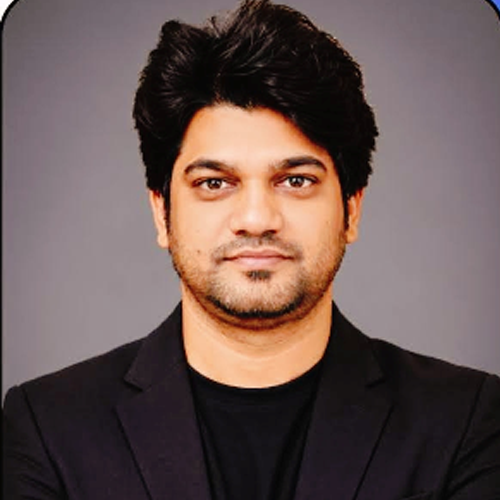
Saurabh Mishra
Saurabh Mishra is a Cloud Evangelist with a deep passion for cloud architecture, DevOps, and automation. Saurabh actively engages with the global tech community, sharing insights on cloud-native technologies, security best practices, and multi-cloud strategies.As an experienced speaker and mentor, Saurabh has delivered sessions at conferences, meetups, and workshops, helping teams accelerate their cloud adoption, modernization, and optimization journeys. His work bridges innovation and practical implementation, empowering organizations to build resilient, scalable, and secure cloud solutions.