
Breaking Boundaries: Infostealer Strategies in the App-Bound Encryption Era
Browser-stored credentials, cookies, and payment data are among the most valuable targets for modern infostealers. When Google introduced App-Bound Encryption (ABE), an additional layer of security designed to protect browser-sensitive data, it became a new obstacle standing between infostealers and this data, leaving them with no choice but to find a way to bypass it. Rather than retreating, the infostealer ecosystem adapted quickly, and nowadays virtually every major infostealer bypasses ABE in one way or another. Since the introduction of ABE, we have been closely tracking how threat actors have evolved their techniques in response. In this talk, we share the results of our latest research into the distinct bypass techniques now used in real-world attacks.
We examine the technical implementation of each technique, the privileges and execution conditions it requires, and the operational advantages and limitations it presents to attackers. We also map these techniques to the infostealer families observed using them in the wild, showing how different attackers have made different trade-offs between reliability, complexity, stealth, and portability.
Beyond documenting individual bypasses, our research identifies behavioral patterns shared across otherwise distinct implementations. These commonalities offer concrete opportunities for detection and threat hunting.
In this presentation, we will cover:
- The security model and motivation behind ABE
- A comprehensive breakdown of ABE bypass techniques observed ITW
- A mapping of these techniques to known real-world infostealer families
- The attacker prerequisites, required privileges, limitations and operational trade-offs involved
- Shared behavioral patterns that can support detection and threat hunting
Attendees will leave with a thorough understanding of the current ABE bypass landscape, how infostealers have adapted to it, and the detection opportunities it opens for defenders.
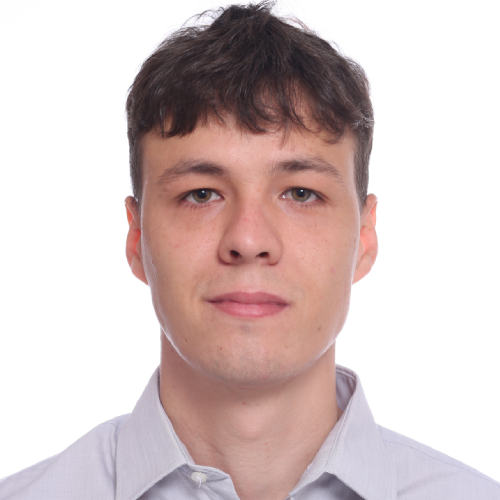
Vojtěch Krejsa – Gen Digital
Vojtěch Krejsa is a Threat Researcher at Gen Digital, where he specializes in tracking and analyzing information stealers and data-theft related threats. Driven by a genuine passion for reverse engineering and malware hunting, he is always eager to dig deep into how things truly work under the hood.
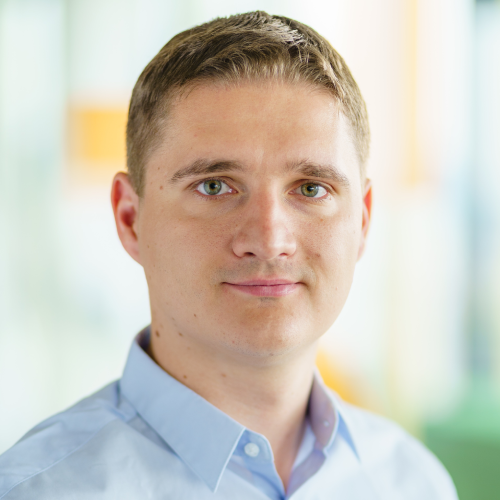
Jan Rubín – Gen Digital
Jan Rubín is a Threat Research Team Lead at Gen Digital, specializing in information stealers, cryptocurrency-related threats, and crimeware. He leads a focused research team dedicated to analyzing and disrupting these threats.
Beyond his work at Gen Digital, Jan is a guest lecturer in reverse engineering at the Czech Technical University in Prague, a frequent cybersecurity conference speaker, and an active mentor. He contributes to the cybersecurity community through education, mentoring, and knowledge sharing.