Poisoning the Well: Deconstructing Next-Gen Supply Chain Attacks and the Myth of Code Trust
Enterprise perimeters have not vanished; they have shifted into the third-party software repositories, CI/CD pipelines, and open-source dependencies that fuel modern development. Supply chain attacks have transformed from occasional, highly targeted state-sponsored operations into an industrialized scourge. Threat actors are aggressively exploiting deep-seated trust models through malicious dependency confusion, typo squatting, code signing certificate theft, and automated pipeline injection. When malware arrives wrapped in a valid vendor signature or nested deep inside an updated enterprise dependency, traditional signature-based tools and perimeter defenses are effectively neutralized.
This presentation moves past the high-level policy discussions surrounding SBOMs to dissect the raw operational mechanics of supply chain compromises. We will analyze the lifecycle of recent high-profile pipeline breaches, detailing how attackers quietly insert malicious payloads into trusted software delivery loops.
Crucially, the session shifts from reactive containment to proactive detection. We will deliver actionable frameworks for building supply chain resilience, including behavioral analysis strategies that catch anomalous post-update activity, practical integrity verification models for containerized pipelines, and techniques for leveraging AI and ML models to spot malicious anomalies within massive dependency graphs. Attendees will leave with practical engineering strategies to verify, monitor, and defend software infrastructure under the assumption that the upstream supply chain is already compromised.
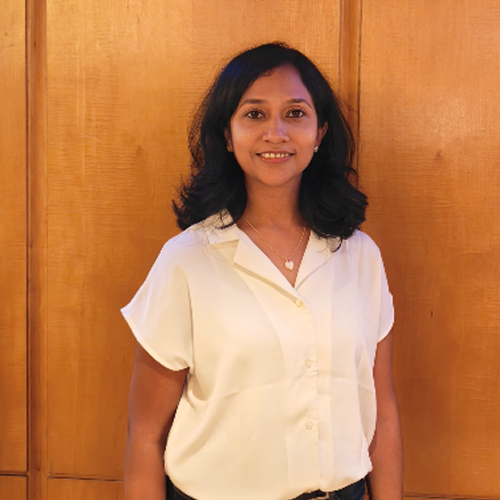
Meghna S Reddy – Dell Technologies
Cybersecurity Governance Leader and Architect with 16+ years of experience leading security strategy, architecting secure-by-design systems, VAPT Governance, Secure Development Lifecycle (SDL) enforcement, and enterprise compliance initiatives across Software, Firmware, Platform and Embedded ecosystems. Trusted advisor driving measurable risk reduction, audit readiness, and security transformation across product portfolios using Agentic workflows.