
Weaponizing Trust: An Analysis of TeamPCP’s Cross-Platform Multi-Wave Supply Chain Attacks
Software supply chain attacks have become a major threat to software distribution ecosystems. This talk microscopically examines the TTPs of TeamPCP, a sophisticated threat actor that has pioneered several novel techniques to infiltrate Windows, Linux, and macOS environments. Within the last year, TeamPCP has conducted multiple campaigns targeting widely-used open-source repositories, including npm and PyPI, compromising packages associated with popular projects like Trivy, LiteLLM, and Mistral AI.
These operations have evolved across distinct campaigns, each resembling a new wave, each introducing new credential theft capabilities or execution techniques.
The first wave, Shai-Hulud, harvested developer credentials to abuse compromised accounts (poisoning trusted repositories, enabling autonomous propagation) and deployed redundancy mechanisms capable of falling back to GitHub repositories when primary command-and-control channels failed.
The second wave, Mini Shai-Hulud, abused a compromised Python package to silently download and deploy the Bun JavaScript runtime as its execution environment.
The third wave, Hades/Miasma, shifted away from conventional npm preinstall and postinstall script abuse, instead exploiting configuration files used by the node-gyp build system, incorporating one-time execution guards and memory-based credential extraction techniques.
Additionally, these campaigns leveraged prompt injection techniques to evade AI-assisted code analysis and security systems, reflecting an emerging trend of adversaries explicitly targeting AI-enabled defensive workflows.
As the attacks progressed through these waves, TeamPCP also collaborated with the Ransomware-as-a-Service (RaaS) group Vect, expanding the operational impact of its compromises. To make matters worse, in May 2026 TeamPCP publicly released its source code, significantly complicating attribution by enabling copycat actors to adopt or modify the original tooling.
This presentation will reconstruct the granular evolution of TeamPCP’s operations, highlighting how its TTPs morphed over successive campaigns. We will provide a detailed technical analysis of their credential-theft capabilities across Linux, macOS and Windows platforms, examine the architectural differences between campaign variants, and discuss defensive strategies for organizations that employ automated build pipelines and AI-assisted security tooling.
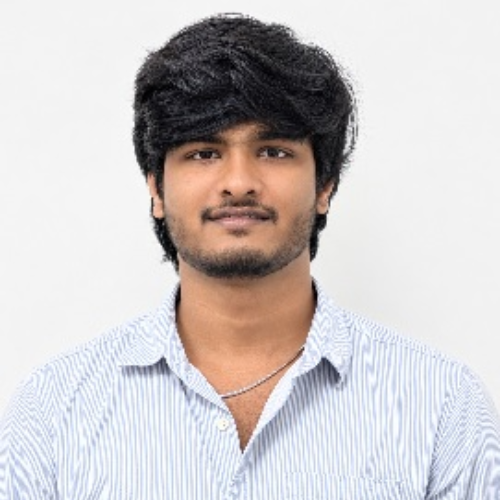
Praveen Babu D – K7 Computing Pvt Ltd
Praveen Babu D is a Threat Researcher with over two years of experience in malware research, reverse engineering and static and dynamic analysis. His expertise spans Windows malware analysis and forensic investigations, as well as macOS malware research. He specializes in generic detection development, incident response, and emerging threat research, and actively contributes to the cybersecurity community through technical blogs.
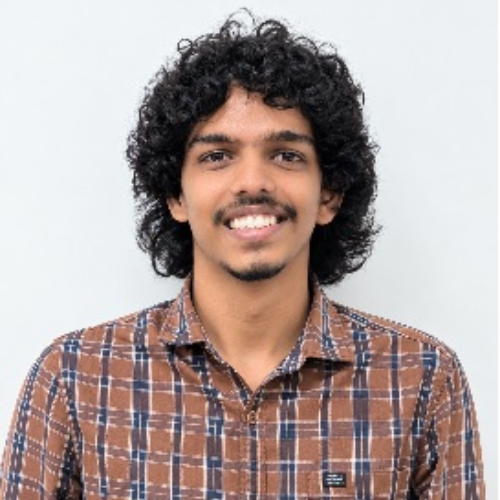
Srinivasan E – K7 Computing Pvt Ltd
Srinivasan E is a Threat Researcher with hands-on experience in malware analysis, reverse engineering, and incident response across Windows and Linux environments. His skills include static and dynamic malware analysis, threat investigation, and detection research. He analyzes emerging threats and handles security incidents, while also contributing to the cybersecurity community through technical blogs and research.