
Beyond the Implant: Reverse Engineering Native AOT Malware and Exposing a 30,000-Agent Operator Ecosystem
Modern threat actors increasingly rely on custom remote management frameworks that blend legitimate administration capabilities with post-compromise tradecraft. During routine threat hunting within the Cyderes Threat Intelligence Data Lake, we identified a suspicious archive masquerading as a remote management update package. Initial analysis revealed a .NET Native AOT malware family deploying a persistent remote management agent communicating with centralized attacker-controlled infrastructure.
What began as a traditional malware investigation evolved into a rare opportunity to examine the attacker ecosystem from the inside. During analysis of the management platform, we identified weaknesses in the application’s authentication and authorization implementation, including client-side trust assumptions and insufficient server-side validation. These flaws exposed significant portions of the operator infrastructure, providing defenders with visibility that would normally remain inaccessible.
By combining malware reverse engineering, infrastructure analysis, and management platform assessment, we reconstructed the architecture and operational workflows of a mature post-compromise ecosystem. Using Binary Ninja-based WARP signature recovery, runtime string hydration, and behavioural analysis, we recovered a feature- rich implant supporting hidden RDP through termsrv.dll patching, concurrent sessions, HVNC browser access, VNC deployment, RustDesk integration, keylogging, credential collection, remote shell execution, network scanning, screenshot capture, webcam access, and long-term victim management.
We also identified an unusual companion component: a screen-locker disguised as a Microsoft Phone Link synchronization failure dialog. While the locker contains no credential theft functionality, it restricts user interaction and conditions victims to remain engaged with the compromised system. Combined with the resident agent’s visibility into paired-device notifications, SMS messages, authenticator prompts, and banking alerts, the two components together create a practical mechanism for MFA interception and user manipulation.
The exposed infrastructure provided visibility into more than 30,000 registered agents and associated management workflows, revealing deployment automation, command execution history, credential collection mechanisms, operator annotations, victim organization practices, and long-term access procedures. This presentation demonstrates how weaknesses within attacker tooling can become valuable intelligence opportunities for defenders while providing practical insight into Native AOT malware analysis, attacker infrastructure reconstruction, paired-device abuse, and detection opportunities for modern RMM-based intrusion frameworks.
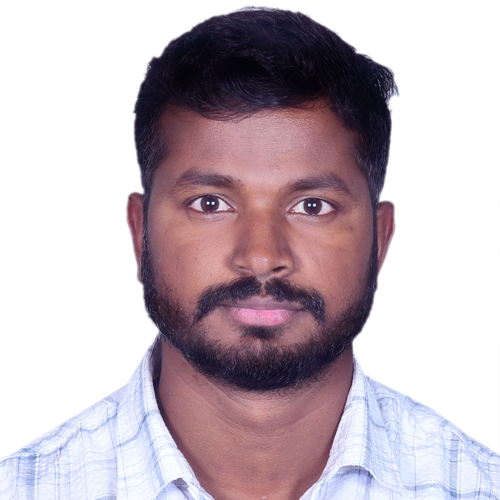
Baskar M – Cyderes
Baskar M is a Senior Threat Researcher at Cyderes with 10 years of experience in cybersecurity, specializing in malware analysis, reverse engineering, threat hunting, and attacker infrastructure investigations. His research focuses on emerging threats, malware ecosystems, and analyzing attacker tradecraft and operational workflows across the post compromise lifecycle.
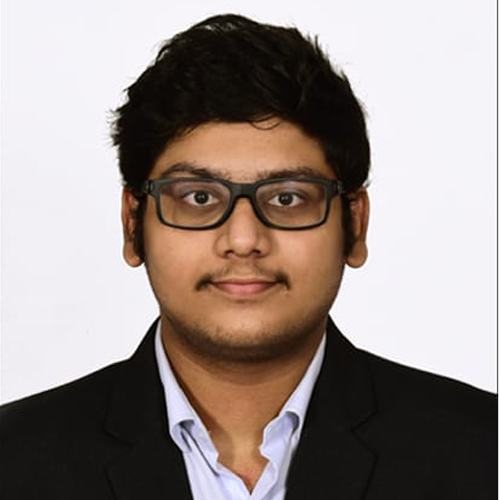
Rahul Ramesh – Cyderes
Rahul Ramesh is a Senior Threat Researcher with Cyderes Howler Cell, specializing in malware analysis, threat hunting, and threat intelligence. He has previously contributed to security research at K7 Computing and SentinelOne. His work focuses on identifying and researching emerging threats, with a particular interest in malware reverse engineering, tracking evolving threat actor payloads and techniques, and contributing to the detection of emerging threats.