
A Familiar Face: Analysis of a new Sharp Panda attack campaign
In early 2026, during an incident response engagement, Viettel Cyber Security identified a malicious loader assessed with moderate confidence to be associated with the Sharp Panda threat actor. The malware was disguised as a legitimate document and utilized a decoy document to mask its malicious activity, tricking victims into executing the payload while presenting expected content. Successful execution enabled the threat actor to establish an initial foothold within the targeted environment.
Subsequent investigation and threat hunting activities uncovered additional malicious samples employing similar tactics using lures and decoy documents. Analysis of the recovered decoy content revealed themes related to government agencies, diplomatic affairs, and other organizations across South and Southeast Asia. Critically, the content and contextual references within these documents indicate that India has been a primary and sustained target of this activity. The targeting of Indian government and diplomatic entities, combined with lures referencing other nations across the region—including Vietnam and the Philippines—suggests that the activity forms part of a broader, coordinated series of campaigns conducted by the threat actor since at least 2024. India’s strategic significance in regional geopolitics and its expanding digital infrastructure make it a high-value target for state-aligned espionage operations of this nature.
The 5.t loader is a well-known malware family that has been extensively used by Sharp Panda in cyber espionage operations targeting a wide range of entities throughout South and East Asia. India, in particular, has featured prominently in Sharp Panda’s targeting scope, alongside Vietnam, Malaysia, and other nations. Historically, the malware has often been deployed alongside RoyalRoad weaponized documents, which exploit vulnerabilities in the Microsoft Equation Editor to deliver payloads such as VictoryDLL and the Soul framework. In this campaign, however, the threat actor adopted a different delivery mechanism while maintaining several operational characteristics previously associated with Sharp Panda activity. Following initial access, the attackers deployed Cobalt Strike beacons from compromised legitimate infrastructure located across multiple countries to facilitate command-and-control communications and post-exploitation operations.
This talk presents a technical analysis of the malware, decoy documents, and supporting infrastructure associated with the campaign, with particular focus on the targeting of Indian entities. We examine the observed tactics, techniques, and procedures (TTPs), evaluate the evidence linking the activity to Sharp Panda, and analyze the threat actor's targeting patterns—with emphasis on how India fits within the broader espionage operation across South and Southeast Asia. Our findings provide insight into an active espionage campaign directed at India and the wider region, and highlight the continued evolution of Sharp Panda’s tooling, infrastructure, and operational tradecraft.
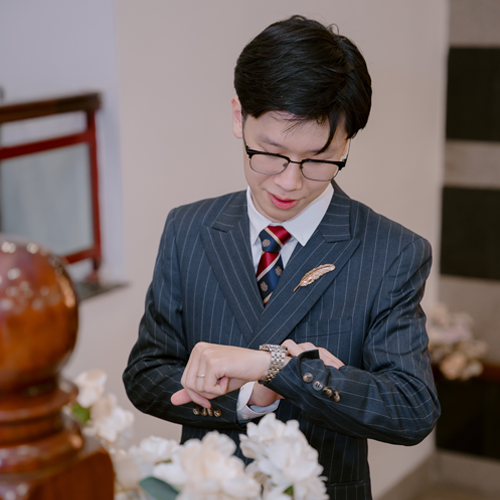
Mr Nguyễn Đức Kiên – Viettel Cyber Security
Nguyen Duc Kien is a malware analysis at Viettel Cyber Security. He has been a reverse engineering for 5 years.
He has specialty in reverse engineering obfuscated malware sample from many threat actors group such as Earth Krahang, Earth Estries, Earth Lamia, Sharp Panda. He also research to unpack, reverse engineering android protected malware and .Net malware protect by commercial protector.
He is also contributor of mwemu, a tool for emulating x86 binary sample and Luc-Nhan, a fork of rikugan for analysing malware in IDA using AI.
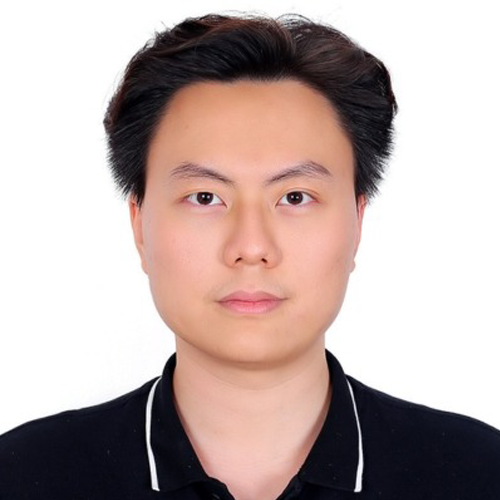
Mr Đoàn Minh Long
Doan Minh Long is a threat analyst with experience in reverse engineering, malware analysis, and tracking threat actors targeting the Southeast Asia region.